 Data room
Encryption spec
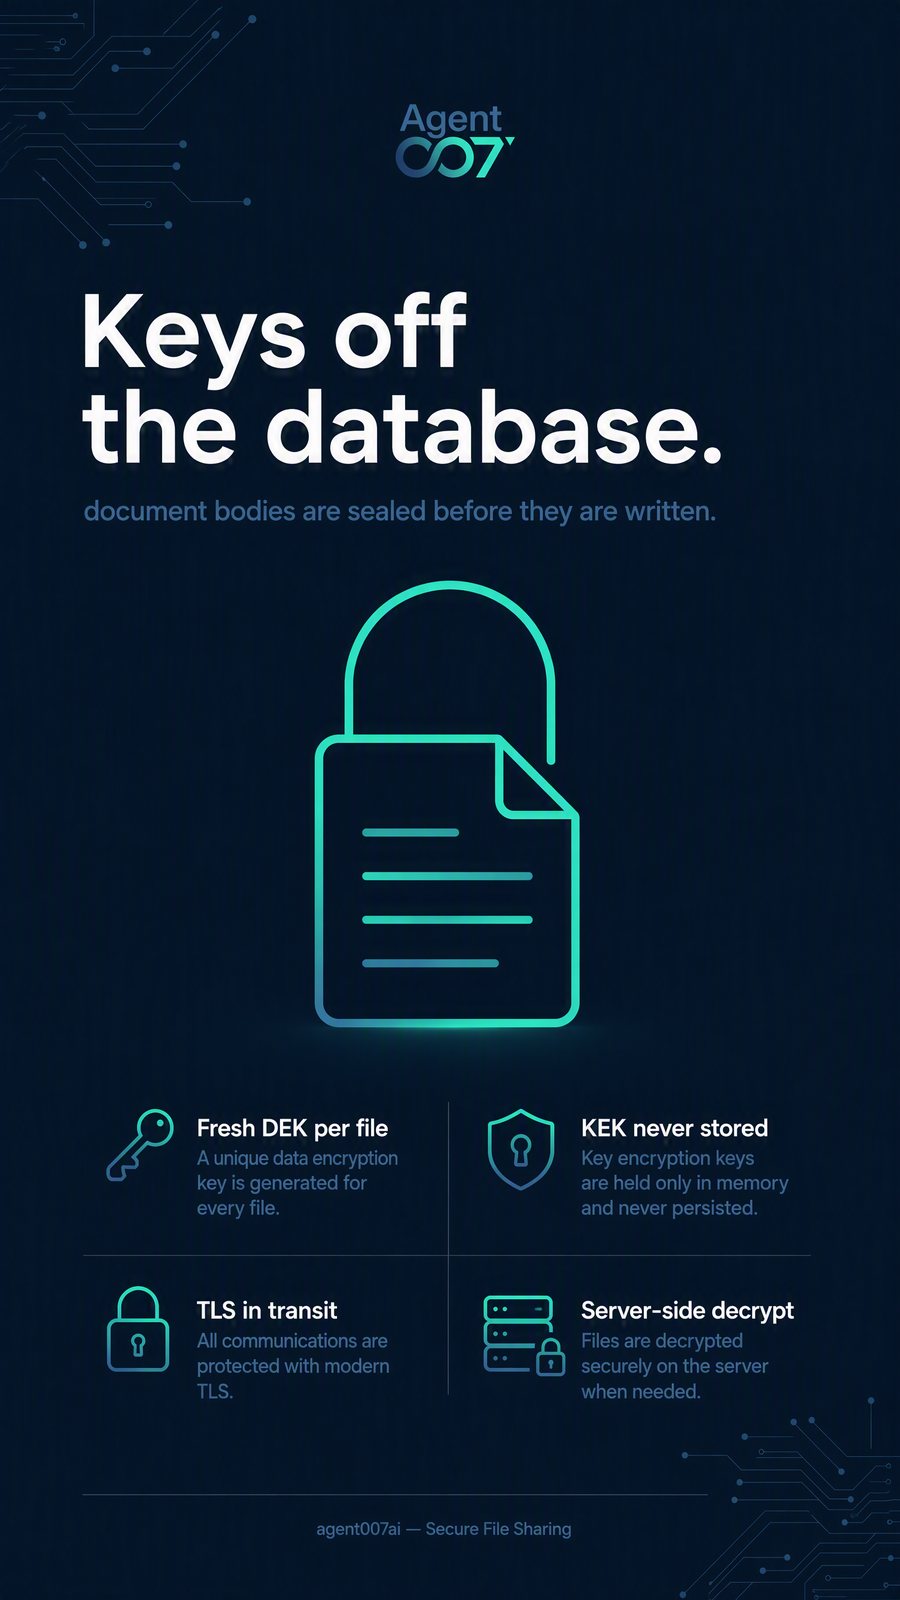
AES-256-GCM. Keys off the database.
Document bodies are sealed before they are written. A leaked database without the master key cannot read the paper. An authorised viewer still sees plaintext. A photograph of the screen still works. That is also true of ShareFile.
- Cipher
- AES-256-GCM (256-bit key, 96-bit nonce, 128-bit tag)
- Per document
- Fresh data-encryption key (DEK) minted for each file
- Master key
- KEK derived from a server secret. Never written to Postgres. Not a customer-managed key. Not a dedicated KMS.
- At rest
- Ciphertext + wrapped DEK in the database. Titles stay in the clear so the index can be walked.
- In transit
- TLS on the public site
- Decrypt
- In memory, on the server, for an authorised viewer. The browser never receives the KEK.
- SOC 2 / ISO 27001
- No. We will not claim it.
- HIPAA / BAA
- No. Do not put PHI in this room.
- Zero-knowledge
- No. Same model as a typical VDR: the desk can open a file for someone who is allowed in.
Signed-in members can walk the same paper inside the Trust Center (Compliance & data security). This page is the public version — the one a lawyer can read without an account.